The Blue Team: How Cybersecurity Experts Protect Our Networks

發布日期:2026-09-05 高中英文篇 Level 2
The Blue Team: How Cybersecurity Experts Protect Our Networks
01

About This Article

關於這篇文章
背景
隨著網路攻擊手法不斷演進,企業保護數位資產的壓力也越來越大。資安團隊通常分為「紅隊」(模擬攻擊者)與「藍隊」(負責防禦),兩者合作找出系統弱點並強化防護。本篇以資安專家陳博士的工作為主軸,介紹企業如何透過系統化程序與人工智慧防禦網路威脅,適合對科技與資訊安全感興趣的高中生閱讀。
  • 陳博士指出企業面臨的網路攻擊威脅日益嚴峻
  • 藍隊測試是找出系統弱點並擬定防禦策略的常用技術
  • 資安程序從建立完整網路地圖開始,並導入 AI 偵測威脅
  • 越來越多企業報名資安培訓,資安人才需求持續成長
  • 嚴格來說,保護數位世界是每個人都應重視的責任
02

Listen First

先聽文章
00:00 / 00:00
03

Reading

閱讀文章
English

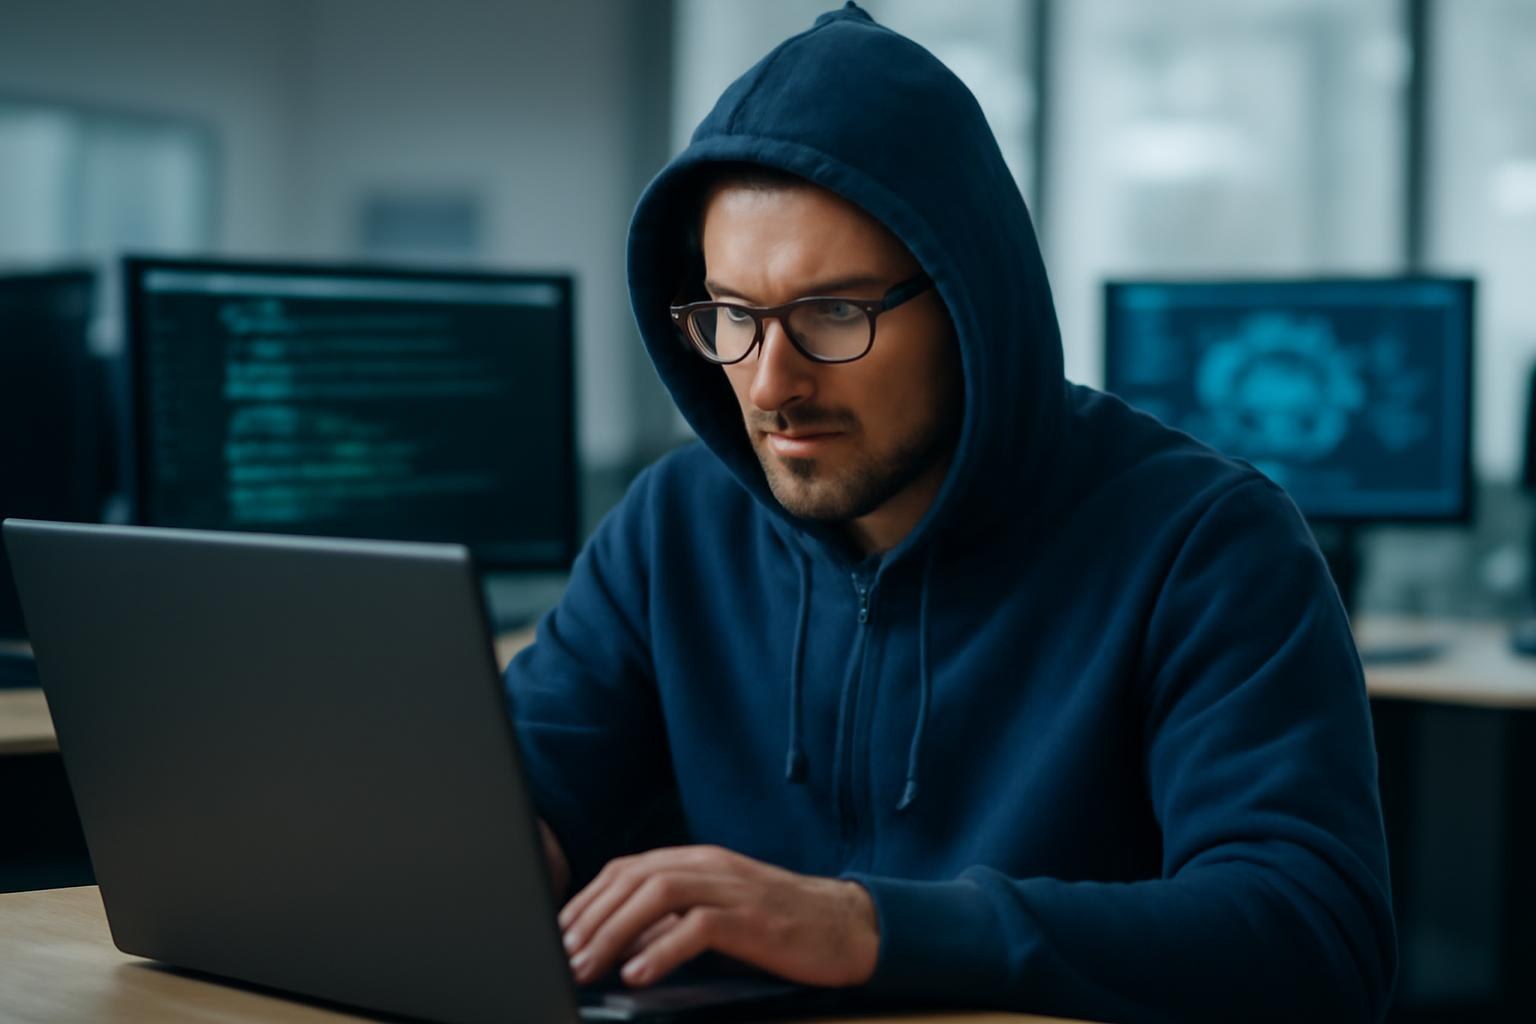
In a recent statement, Dr. Emily Chen, a cybersecurity expert at a technology company in Taipei, referred to the growing challenge of protecting computer networks from online attacks. She admitted that even large organizations can easily lose important data if they do not take the following steps seriously: updating software to the latest version, removing old files, and training staff to obtain better security habits.

To determine the best defence strategy, Dr. Chen's team attempts to study how hackers think. They look for specific weak points in a network by running detailed tests on each physical server. One popular technique is called "blue team testing," where security experts act as defenders to see how well a system responds to a real attack. After testing, the team comes to an agreement on which areas need the most improvement.

The procedure begins with building a complete map of the entire network. This map shows every cell of data flowing through the system. Experts then load a monitoring program onto each connected device to track unusual activity. Dr. Chen explained that her team uses a special version of artificial intelligence that can detect threats before they cause serious damage to the system.

Taking a stand against cybercrime requires both knowledge and effort. More companies are now signing up for advanced security training programs to protect their systems. Dr. Chen noted that students who understand both the physical and digital sides of technology are in high demand in today's job market.

Strictly speaking, the future of our online world depends on the next generation of cybersecurity professionals. For anyone interested in this field, the first step is to learn the basic techniques and understand the tools used by security teams. Whether you are a student or a working professional, protecting our digital world is a challenge that everyone should take seriously.

中文翻譯

近期,台北一家科技公司的資安專家陳博士在一份聲明中提到,保護電腦網路免受網路攻擊的挑戰日益嚴峻。她坦承,即使是大型組織,只要不認真落實以下幾個步驟,也很容易遭受重要資料外洩:將軟體更新至最新版本、刪除舊有檔案,以及培訓員工養成更好的資安習慣。

為了判斷最佳的防禦策略,陳博士的團隊嘗試研究駭客的思維方式。他們透過對每台實體伺服器進行詳細測試,找出網路中的特定弱點。一種常見的技術稱為「藍隊測試」,資安專家在其中扮演防禦方,測試系統對真實攻擊的因應能力。測試結束後,團隊會就最需要改進的部分達成共識。

整個程序從建立完整的網路地圖開始,地圖顯示系統中每一個數據單元的流向。接著,專家會將監控程式載入每台連接的設備,以追蹤異常活動。陳博士解釋,她的團隊使用了一個特殊版本的人工智慧,能夠在威脅對系統造成嚴重損害之前便加以偵測。

對抗網路犯罪需要知識與努力。越來越多的企業正在報名參加進階資安培訓計畫,以保護自身系統。陳博士指出,同時了解科技實體面與數位面的學生,在今日的就業市場中非常搶手。

嚴格來說,我們線上世界的未來取決於下一代的資安專業人員。對這個領域有興趣的人,第一步是學習資安團隊使用的基本技術與工具。無論你是學生還是在職人員,保護我們的數位世界都是每個人都應該認真面對的挑戰。

04

Key Words

重點詞彙片語
12 個
05

Expressions

慣用句
5 則
06

Practice

課後測驗
6 題 +討論 2 題
0 /0 題

1 According to Dr. Chen, what can happen if organizations do not follow the correct security steps?
答對了! 答錯了,正確答案以綠色標示。
2 What is the main purpose of "blue team testing"?
答對了! 答錯了,正確答案以綠色標示。
3 The begins with building a complete map of the entire network.
答對了! 答錯了,正確答案以綠色標示。
4 They look for weak points in a network by running detailed tests on each physical server.
答對了! 答錯了,正確答案以綠色標示。
5 More companies are now advanced security training programs to protect their systems.
答對了! 答錯了,正確答案以綠色標示。
6 After testing, the team on which areas need the most improvement.
答對了! 答錯了,正確答案以綠色標示。

Discussion

問題與討論
2 題

以下問題沒有標準答案,請試著用英文說出自己的想法,一題講三到五句話。

  1. 1 Dr. Chen says that students who understand both the physical and digital sides of technology are in high demand. Would you consider a career in cybersecurity? What skills do you think are most important for this kind of work?
  2. 2 Have you ever worried about your personal information being stolen online? What steps do you take to protect your data, and what more do you think companies should do to keep users safe?